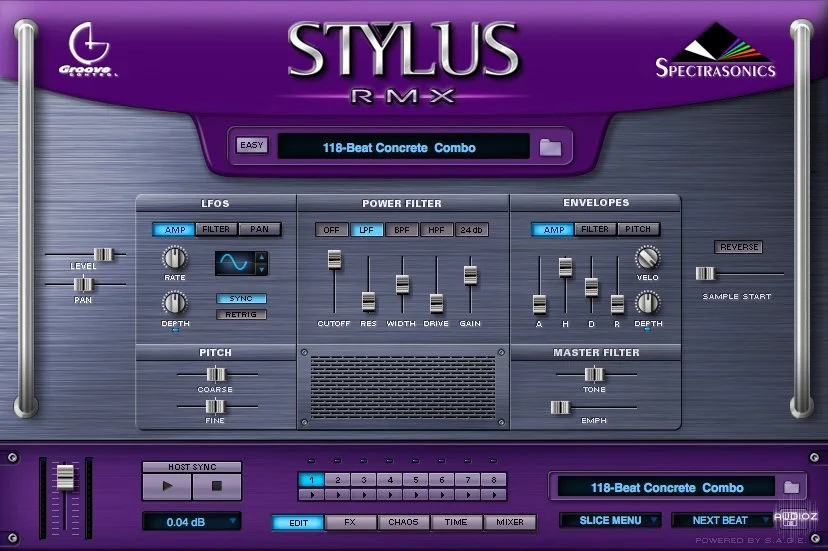
Spectrasonics Stylus RMX v1.10.1e Incl Patched and Keygen READ NFO-R2R
Sylus RMX is a completely new groove-based virtual instrument plug-in for Macintosh and Windows. Stylus RMX is the first product to offer the combined power of Groove Control with Spectrasonics Advanced Groove Engine (S.A.G.E.) technology giving users dramatic new control over groove production and
资源介绍
Team R2R | 03 Dec 2021 | 20.1MB
Sylus RMX is a completely new groove-based virtual instrument plug-in for Macintosh and Windows. Stylus RMX is the first product to offer the combined power of Groove Control with Spectrasonics Advanced Groove Engine (S.A.G.E.) technology giving users dramatic new control over groove production and performance.
Spectrasonics' in-house development team created the new instrument from the ground up, with dozens of new features including the ground-breaking Chaos Designer, a completely redesigned multi-page user interface, a new core library of sounds, all with a focus on realtime groove creation and performance.
A witch says,
Some crack issue in the previous
v1.10.0f release has been fixed in
this release.
We took another time to check and test
the protection to fix the issue. If you
like technical stuff, check below.
Thanks RET for helping the test phase!
TECHNICAL STUFF - AGAIN
Spoiler:
We've overlooked the one protection (yet complicated) in the last work. This
extra protection kills some of essential function like preset recalling after
triggered. Mostly it is used for another Anti-R2R trick to detect RSA-Key
modification, but there are some hidden checks for non-keygen bypass crack
too.
To detect RSA-Key modification, SS (Spectrasonics) app has RSA encrypted
content inside. It will be decrypted after a while, then some calculation
will be done. If content is corrupted (because RSA-Key is tampered by R2R),
it bombs.
- Encrypted Content + Legit RSA Key = Valid Decrypted Content
- Encrypted Content + R2R RSA Key = Decryption Failed, bombs!
Theoritically, it can be defeated like this :
- Encrypted Content ---[Decrypt by Legit RSA Key]---> Valid Decrypted Content
---[Re-Encrypt by R2R RSA Private Key]---> Encrypted Content for R2R Key
- Then, swap original encrypted content to new re-encrypted one. Done!
However, there are many content, and the content changes by months (1 content
per month = 12 variants available). While it's still possible to swap all
content, the testing phase will be complicated. To avoid that, we injected
some nice code to decrypt the content instead of swapping content :)
We want to explain all the magic tricks SS used - but that will make NFO
too long. If you are a cracker who has interests :
- Check our injected code and how we decrypt the original content :)
- Find their month-magic. SS changes the routine they use by months.
- Search value 0x54B1B. You can find the delay RSA Content Decryption.
- Search value 0x673948DE. It does something like this :
hiddenState = hiddenState XOR decryptedContentVal
XOR hiddenXorVal
XOR 0x673948DE;
if (!isTimebombed) {
if (hiddenState != validValue) {
isTimebombed = true;
}
}
- "hiddenState" is also used by other places. We missed that part
last time!
-
"decryptedContentVal" is changed by months.
-
"hiddenXorVal" is static value but changed by months.
-
"validValue" is not fixed value :)
-
"isTimebomed" is bool value in static memory.
- As we stated in the first paragraph, there are some hidden extra checks
to disable license-check-bypass-cracks. At least you need to know the
license data structure to trace some bombs.
Happy Reversing!
相关推荐

效果器插件
Slate Digital MetaTune v1.2.3.0 U2B macOS 阅读 NFO-GUISEPPEv1.2.3.0
效果器插件
Slate Digital MetaTune v1.2.3.0 WiN 独立 VST2/VST3v1.2.3.0
效果器插件
ArtsAcoustic - Reverb 1.6.0.15、BigRock 1.0.7、CL Series 1.0.19、VST x86 x64(无需安装,SymLink 安装程序)[19.03.2017]
效果器插件